For security leads
Evidence on file, not on request.
Scans on a schedule, risky settings caught before deploy, every change logged.
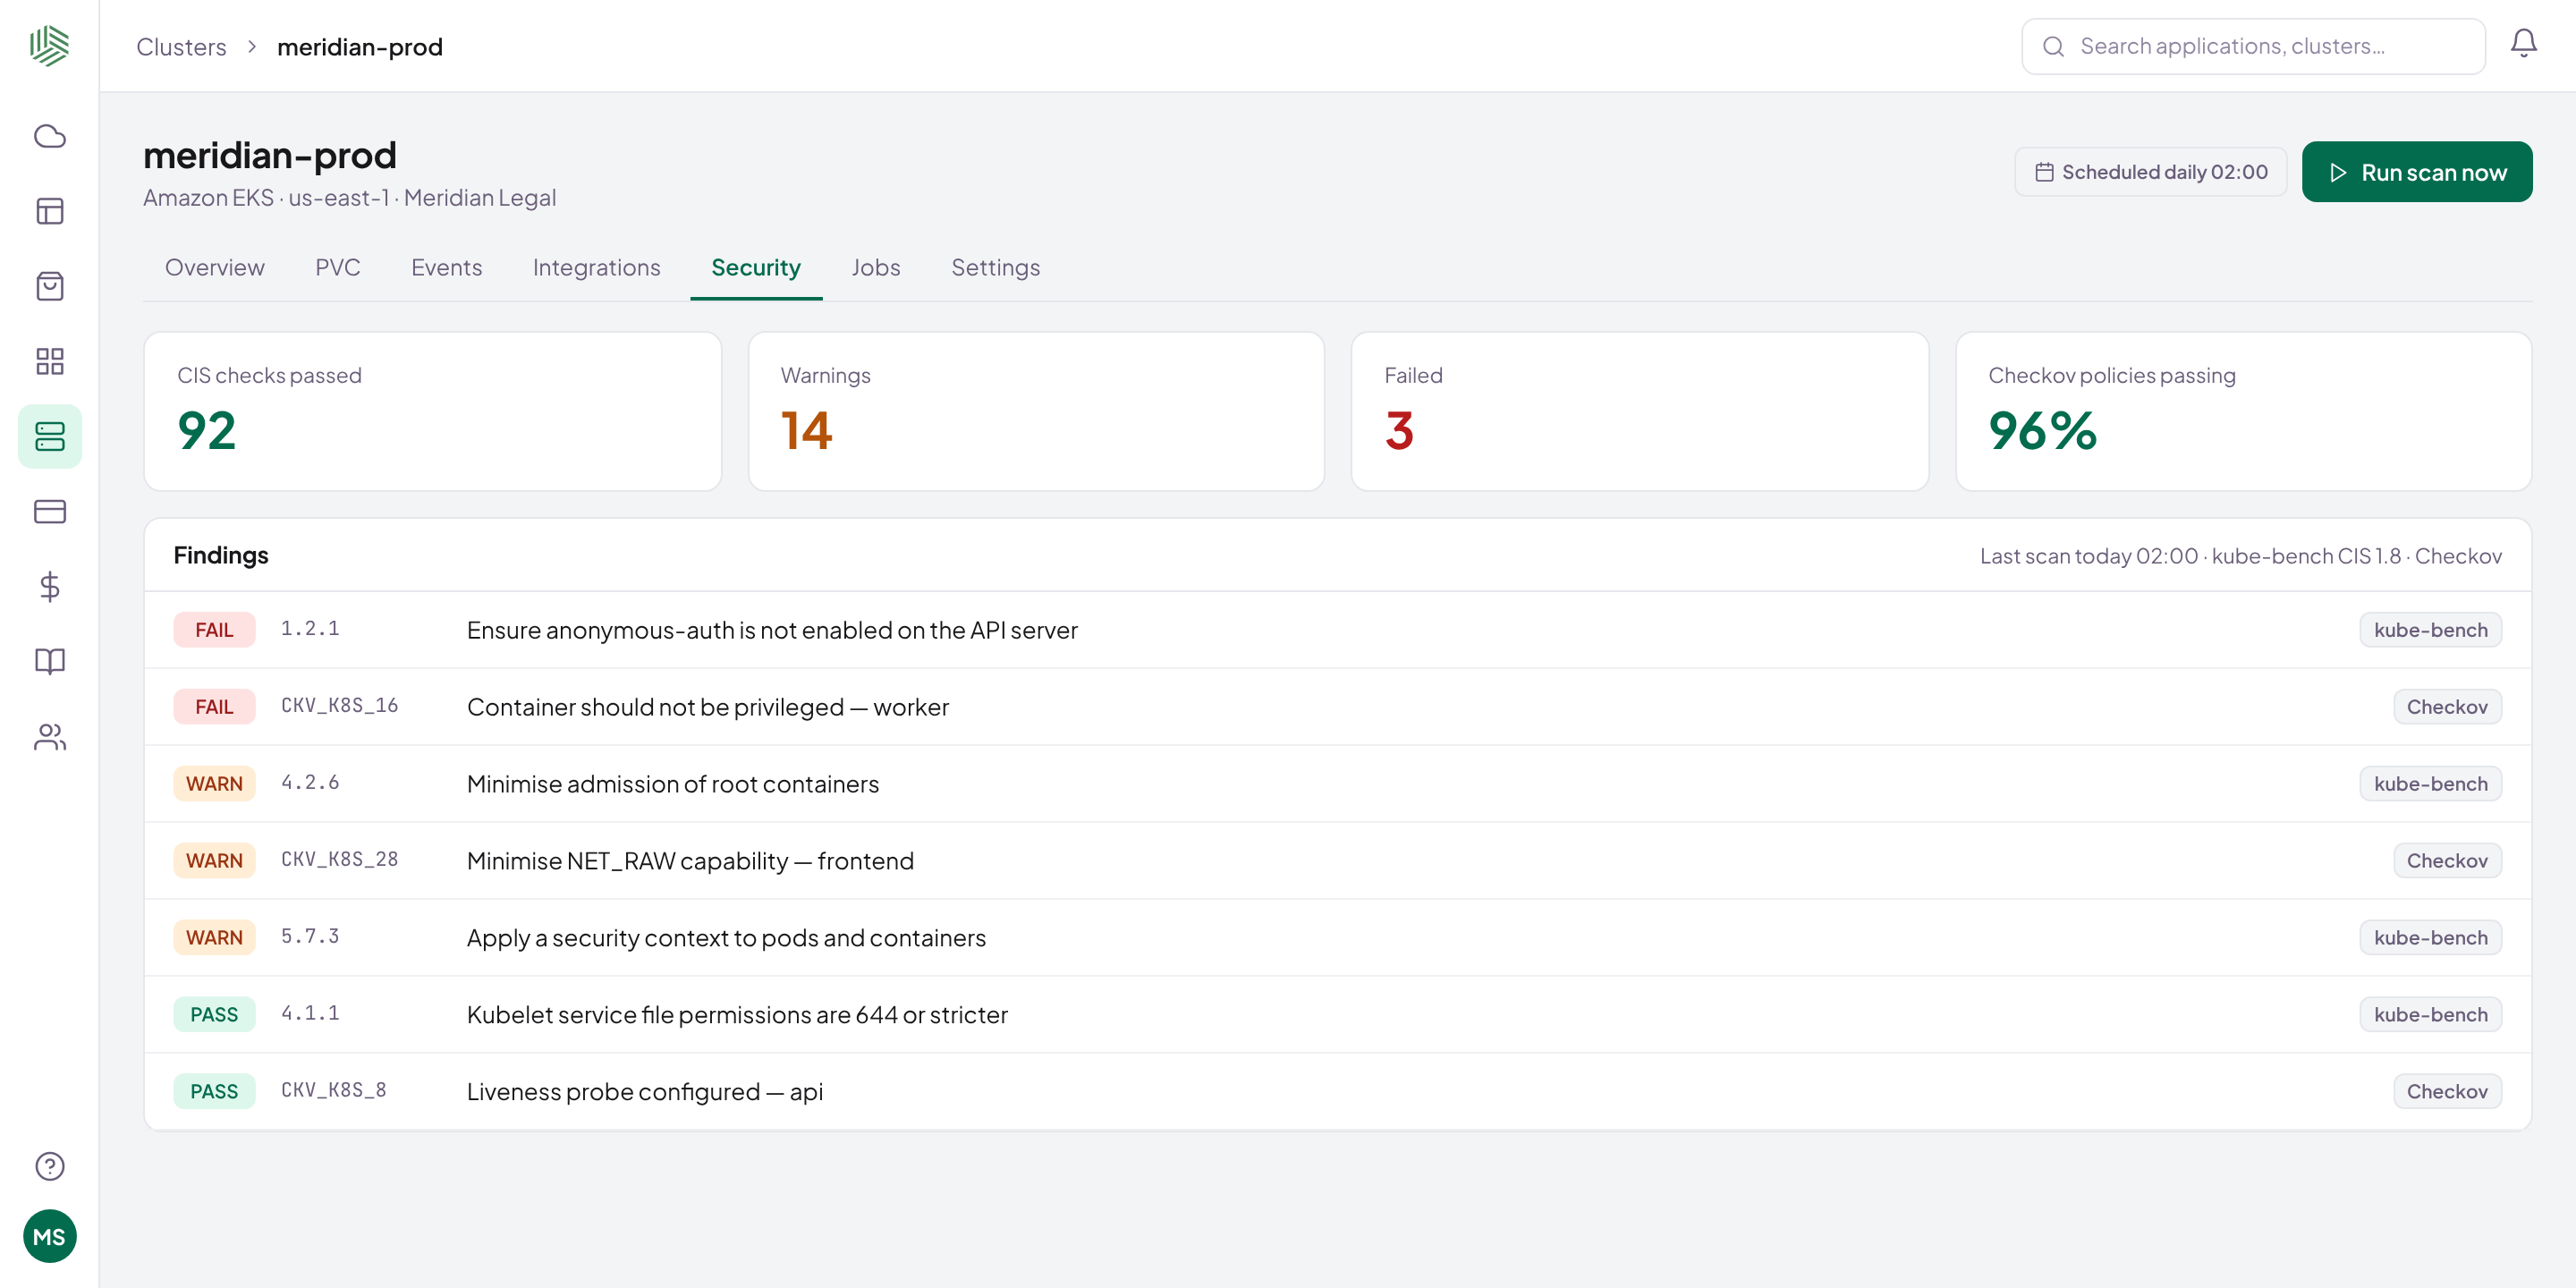
Real Shipfast screen · sample data
Sound familiar?
Security shouldn't be a scramble before audits.
Last-minute evidenceScans run the week before.
Risky settings shipPrivileged containers slip through.
Who changed what?No single record.
Scans
Scheduled CIS and policy scans.
kube-bench and Checkov, on your schedule.
- CIS benchmark per cluster
- Scheduled or on demand
- Results kept for every review
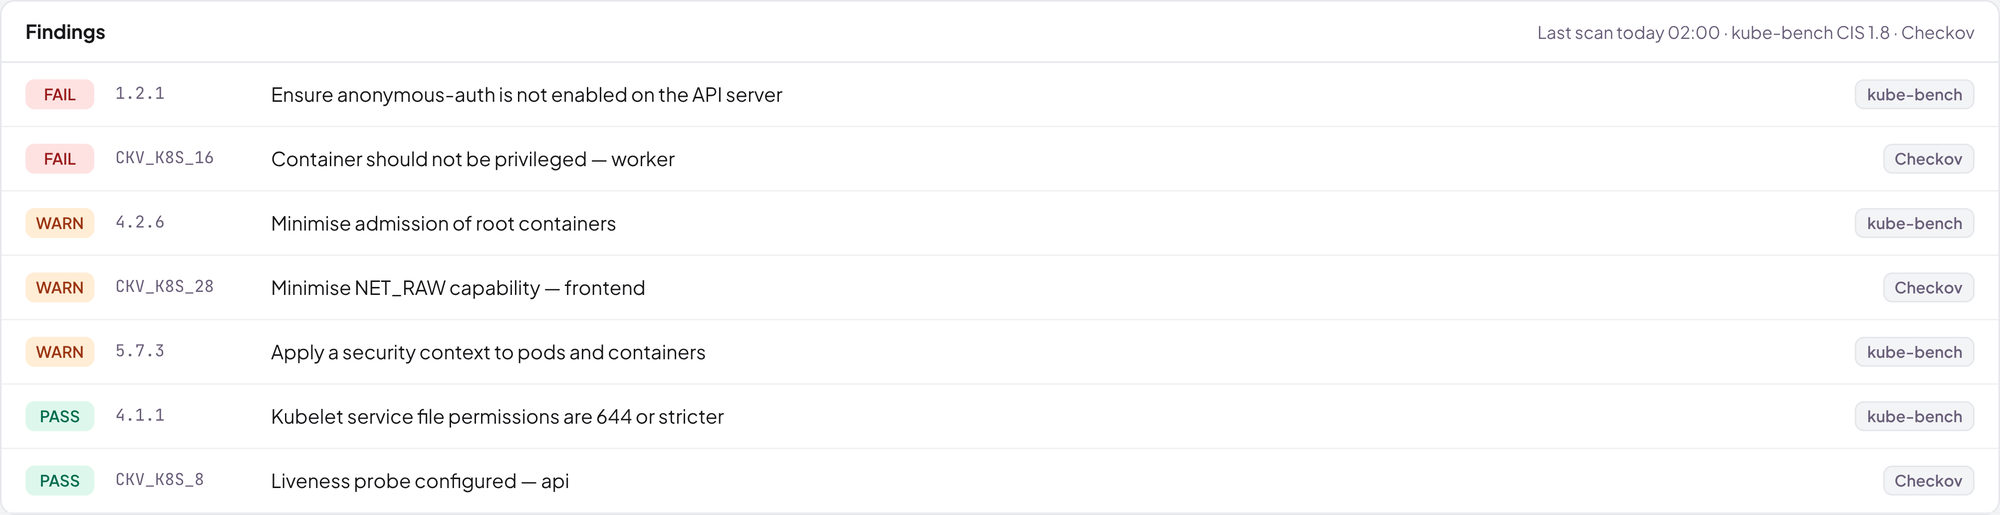
Real Shipfast screen · sample data
Prevention
Stop risky settings before deploy.
kubesec checks every template at render time.
- A clear reason for every flag
- Risky kinds blocked on shared clusters
- Same rules for every team
Render check · workerkubesec
spec: containers: - name: worker securityContext: privileged: true
BlockedPrivileged container. Remove
privileged: true to continue.IllustrativeChecked before it reaches a cluster
Access and audit
Who did what, with the diff.
Sign-in, roles and API keys in one place.
- Keycloak SSO and GitHub sign-in
- Roles for create, deploy, approve and view
- Activity log with a diff for every change
Activity logtoday 11:42 · Asha (DevOps)
Changedclient-portal · productionvariables
- WORKER_MEMORY: 512Mi+ WORKER_MEMORY: 1Gi- API_REPLICAS: 3+ API_REPLICAS: 4
IllustrativeEvery change, with a diff
What changes
Same people. Less toil.
Show security posture
BeforeAd-hoc scans, if anyAfterScheduled scans with history
Catch risky settings
BeforeManual review, sometimesAfterChecked at render, every time
Answer "who changed this?"
BeforeAsk aroundAfterActivity log with a diff
FAQ
Questions, answered.
Which standards are covered?
The CIS Kubernetes benchmark via kube-bench, plus Checkov policies and kubesec checks.
Can we use our identity provider?
Yes, through Keycloak single sign-on, or GitHub sign-in.
Is every change recorded?
Yes, with who made it, when, and a diff.
Does a green CIS report mean we are secure?
No. It covers cluster configuration; application code and image vulnerabilities need their own tools.
Now onboarding pilot teams
Ready to ship faster?
Bring one app. We'll connect a cluster and ship a release with you.