Security built into how Shipfast runs.
Your workloads stay in your accounts, clusters connect outbound, and every change is logged.
Your accounts
Apps run in your accounts, on-prem or air-gapped.
Outbound-only agent
No inbound ports, VPN or bastion host.
Self-hosted option
Keep the control plane inside your walls.
The right people, the right actions.
Access to production follows your policy, not whoever holds the kubeconfig.
SSO
Keycloak and GitHub.
Roles
Per team and per app.
Approvals
Before production.
API keys
For CI and scripts.
Checked on a schedule, caught before deploy.
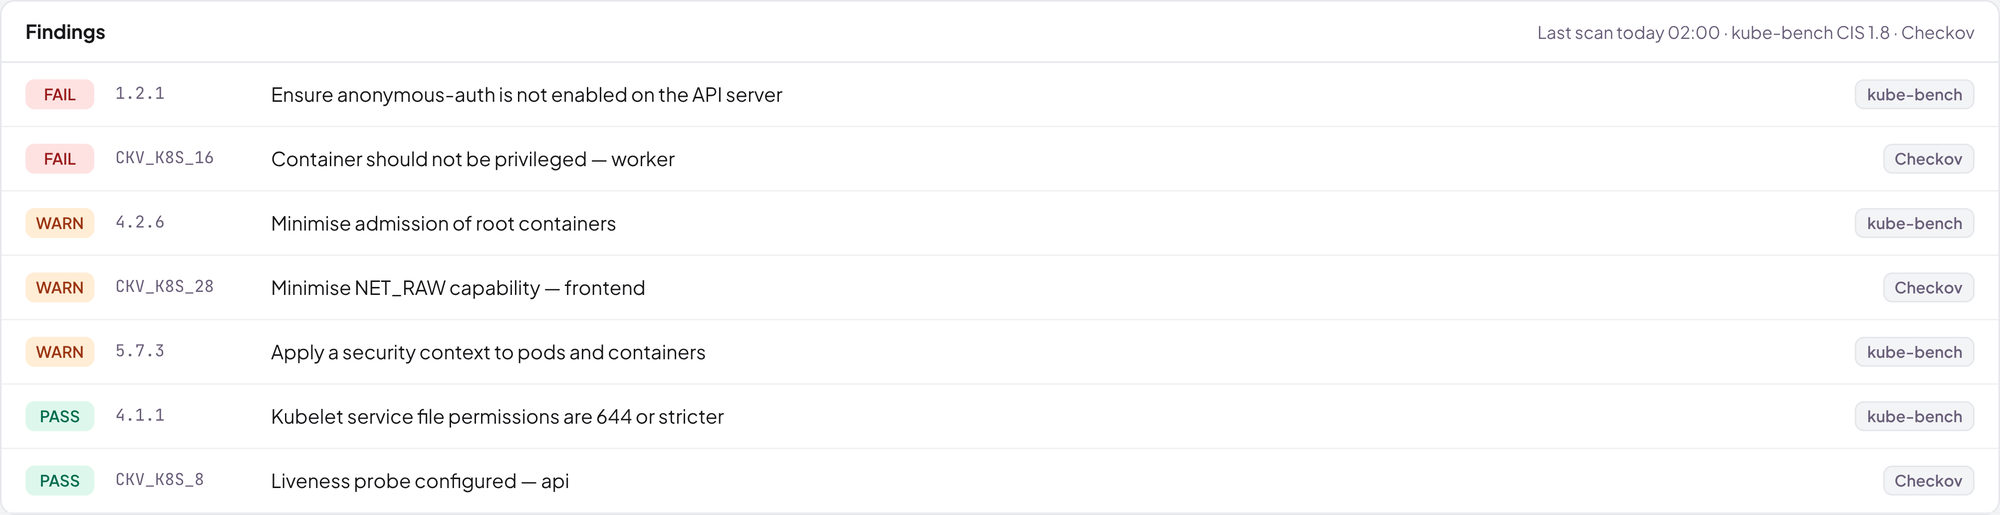
CIS and Checkov scans on your schedule, and kubesec checks at render time.
- kube-bench CIS benchmark per cluster
- Risky settings flagged before deploy
- Results kept for every review
A record of every change. A way back from any of them.
Activity log with diffs
Who, when and exactly what.
Rollback to any revision
Undo a bad release in a click.
Backups switched on
For every environment, from day one.
Documents on request
Questionnaire answers, our sub-processor list and a data processing agreement. Formal certifications are in progress.
Request documentsFound a vulnerability?
Email hello@shipfast.app. We acknowledge reports within two business days.
Ready to ship faster?
Bring one app. We'll connect a cluster and ship a release with you.